How To Use JWT - MUIT-iDev/JWT GitHub Wiki
- Topics
-
- Domain
- {domain}
- Protocol
- https
- Port
- 443
- Exp.
https://domain.name
- Domain
| Category | Method Get | Parameter | Parameter Detail | |
| Query | Header | |||
| Client Authen | /adfs/v1/authen/ | - | GuiAuthKey | |
| /v1/access/ | package | tokenRefresh.GuiAuthKey | ||
| System Authen | /v1/regToken/ | - | token | |
| /v1/access/ | - | SystemAuthKey | ||
| API Verify Signature | /v1/publickey/ | package | tokenAccess.ApiVerifyKey | |
-
- JSON data structure inside the Token after decoding.
-
Token Refresh Payload (
AuthenPayloadRefresh)- Used for requesting a new Token Access without re-authenticating (Expires in 4 hours).
{
  "ProcessId": "uuid-string",      // Unique Identifier (Nonce) for the authentication process
  "Type": "refresh",               // Token type
  "Exp": 17250000000000000,        // Expiration time in DateTime.Ticks format
  "Id": "uuid-string",             // Token Id
  "Staff": true,                   // true = Staff, false = Non-staff / Student / Others
  "SystemKey": "your-system-key",  // System Key of the requesting system
  "Service": "ADFS"                // Authentication Service type (e.g., ADFS, SSO, ThaID)
}
* **Token Access Payload (`AuthenPayloadAccess`)**
* Used as a Token Access attached to the API Request header (Expires in 3 minutes).
{
  "ProcessId": "uuid-string",
  "Type": "access",
  "Exp": 17250000000000000,
  "Id": "uuid-string",
  "Staff": true,                   // true = Staff, false = Non-staff / Student / Others
  "SystemKey": "your-system-key",
  "Service": "UAS",
  "AccessType": "system",          // Access type (e.g., "system" or "client")
  "NameEn": "John Doe",            // User's English name
  "NameTh": "จอห์น โด",             // User's Thai name
  "Email": ["[email protected]"], // Array of user's emails
  "UID": "1234567",                // User ID (e.g., Student ID or Staff ID)
  "SystemKeyRefresh": "your-system-key"
}
(Note: If the Service is ADFS:ThaID, additional claims like FirstTh, MidTh, LastTh, FirstEn, MidEn, LastEn are included).
-
-
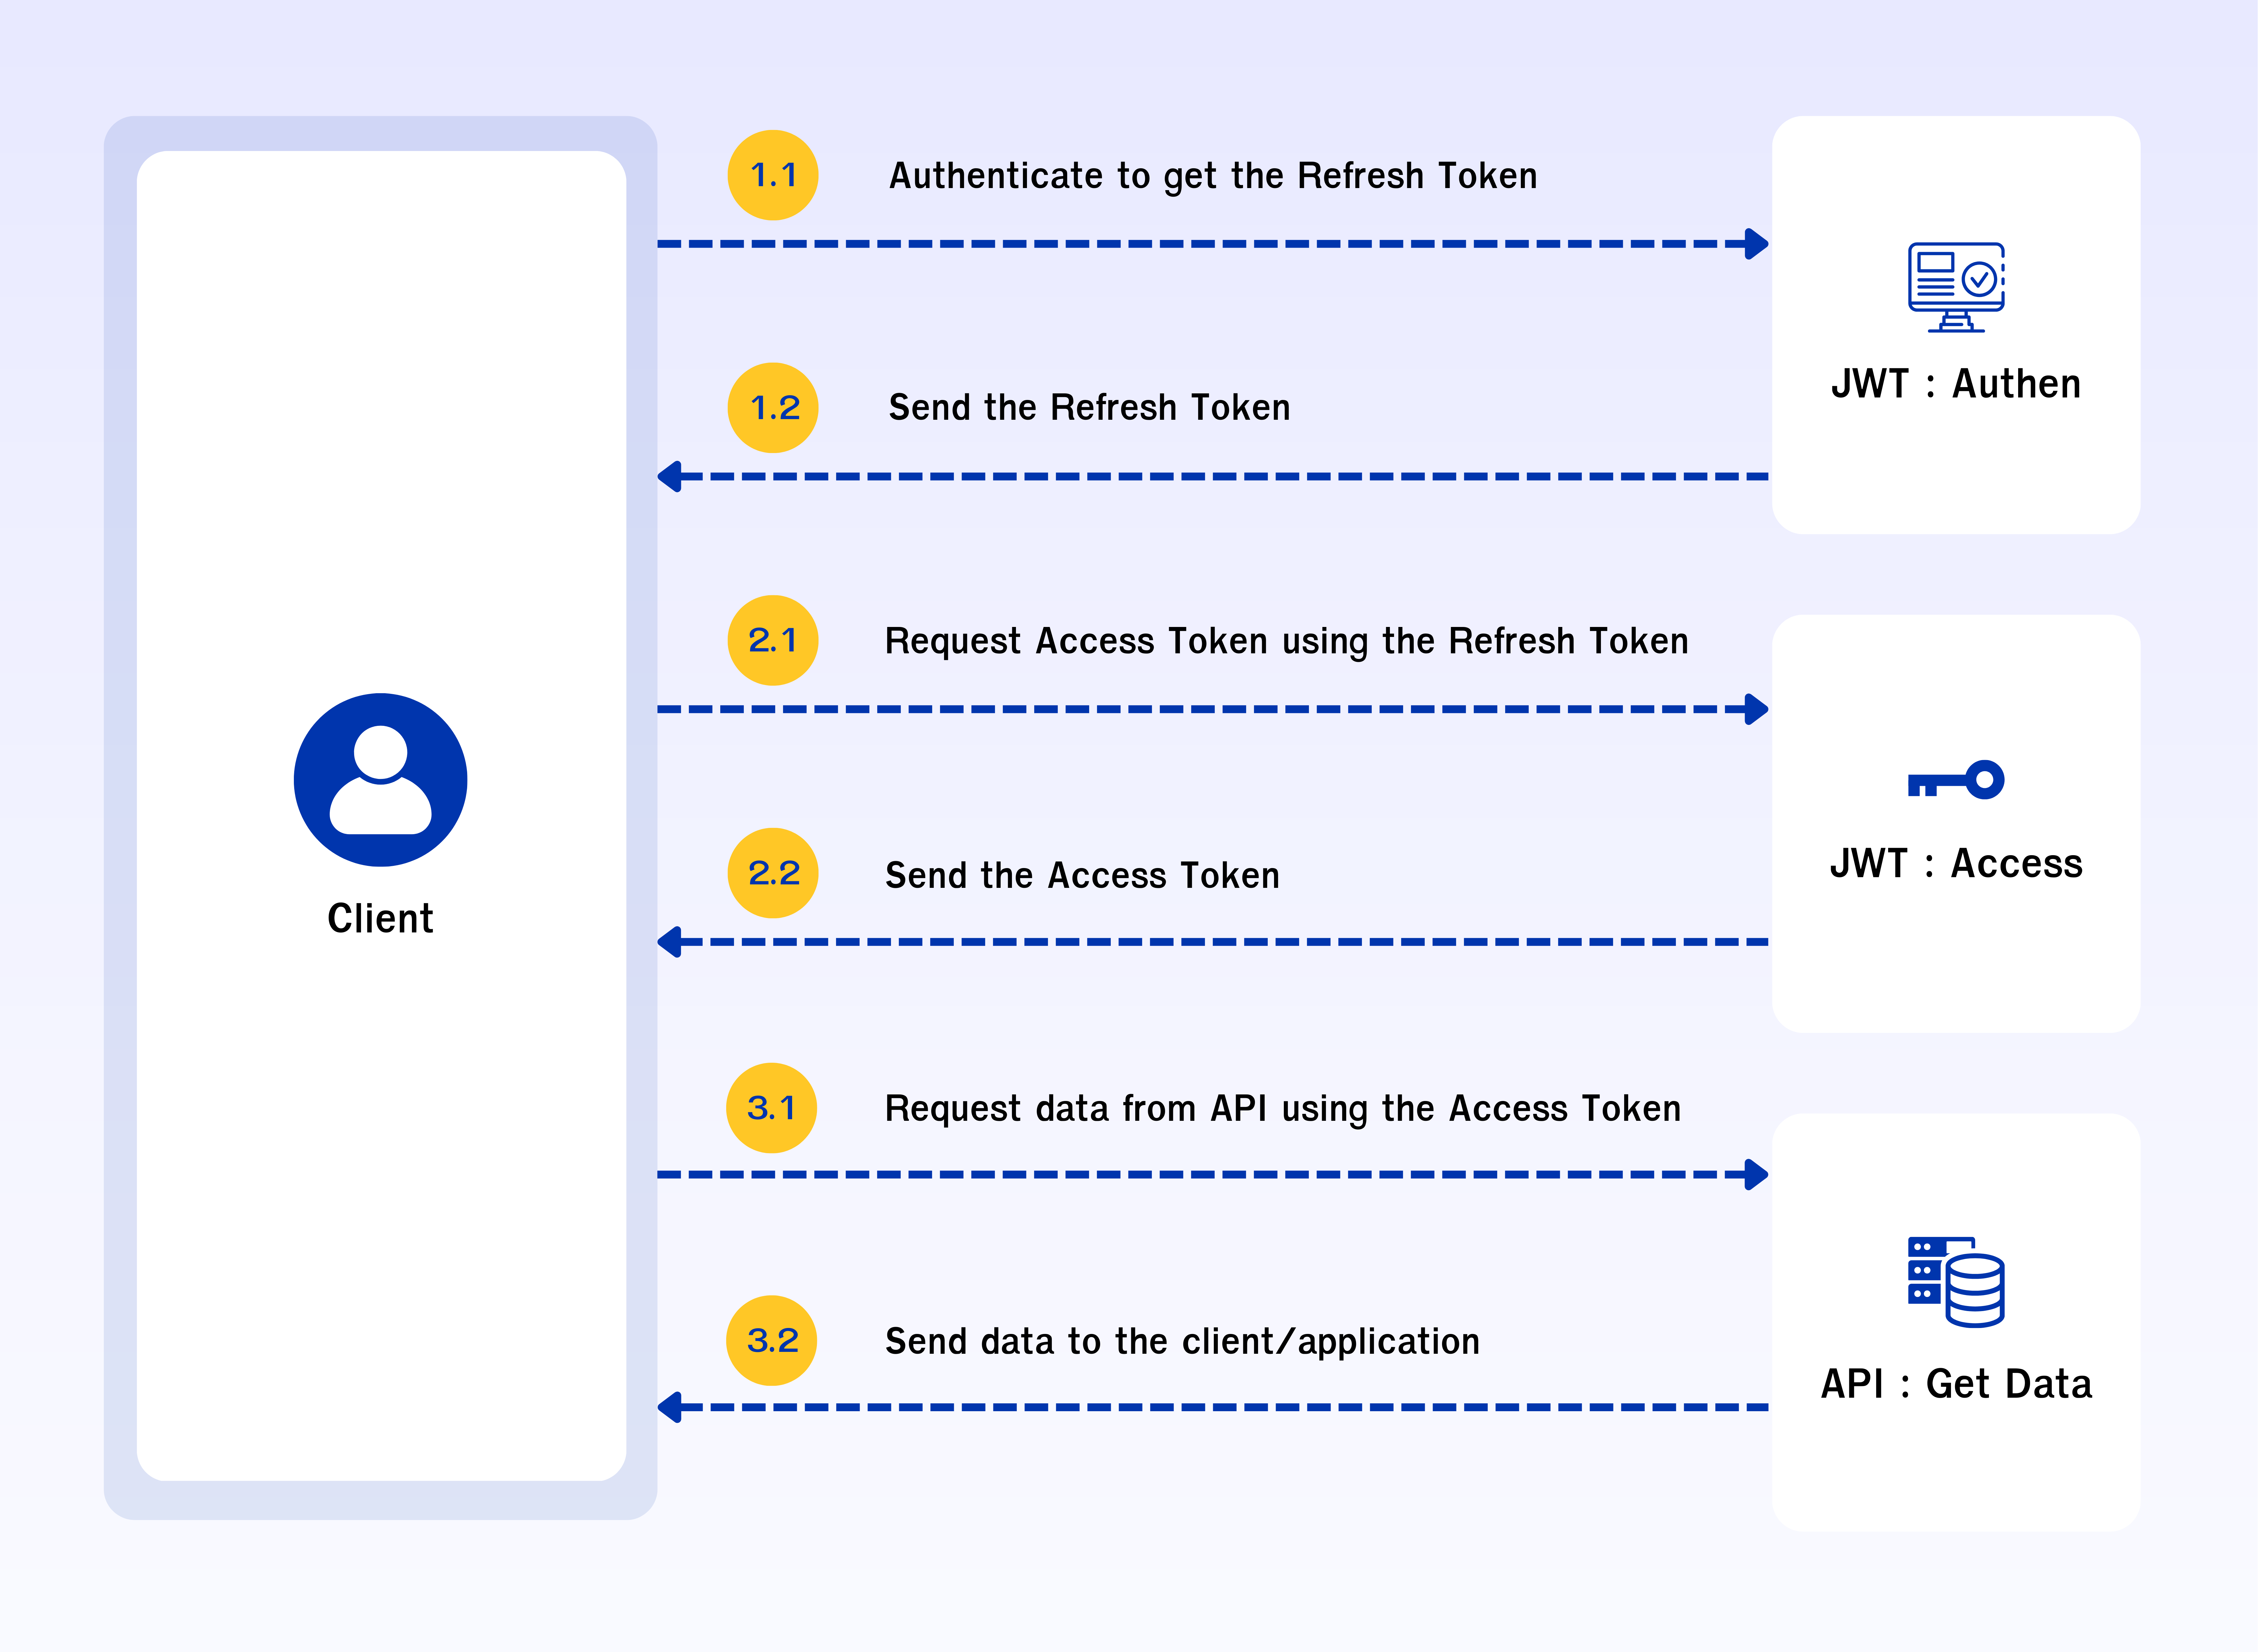
Client use for generate token key.
-
-
- Authen and get token refresh.
- Token refresh has expired in 4 hour.
- Token refresh send to you system, with redirect on method GET.
-
Package
-
systemkey
- System Key.
-
systemkey
-
Example.
- Path
- {domain}/adfs/v1/authen/{GuiAuthKey}
- {domain}/adfs/v1/authen/{GuiAuthKey}?correlationId={UUID}
- {domain}/adfs/v1/authen/{GuiAuthKey}?correlationId={UUID}&option={optional}
- Receive
- you can custom path for receive token refresh and or option.
- {0} is Token refresh.
- {1} is correlationId.
- {2} is option (optional: string empty).
http://localhost:8888/etc/#token={0}&correlationId={1}http://domain.exp/token/{0}/{1}http://your.domain/?token={0}&correlationId={1}http://localhost:8888/etc/#token={0}&correlationId={1}&option={2}http://domain.exp/token/{0}/{1}/{2}http://your.domain/?token={0}&correlationId={1}&option={2}
- Path
- Authen and get token refresh.
-
-
- Get token access, with used token refresh from authen. And get token access for access API.
- Token access has expired in 3 minutes.
- Recommend to use token access for access API in 1 time, and request new token access for use API in next time.
-
Package
- Base64 all parameter, with “.” (dot).
-
tokenRefresh
- Used Data “tokenRefresh” from package authen
-
systemkey
- System Key.
-
Example
- Function generate package
- package = base64({tokenRefresh}.{GuiAuthKey})
- Path
- {domain}/v1/access (package with header)
- {domain}/v1/access?correlationId={UUID}
- {domain}/v1/access?package={package}&correlationId={UUID}
- Function generate package
- Get token access, with used token refresh from authen. And get token access for access API.
-
-
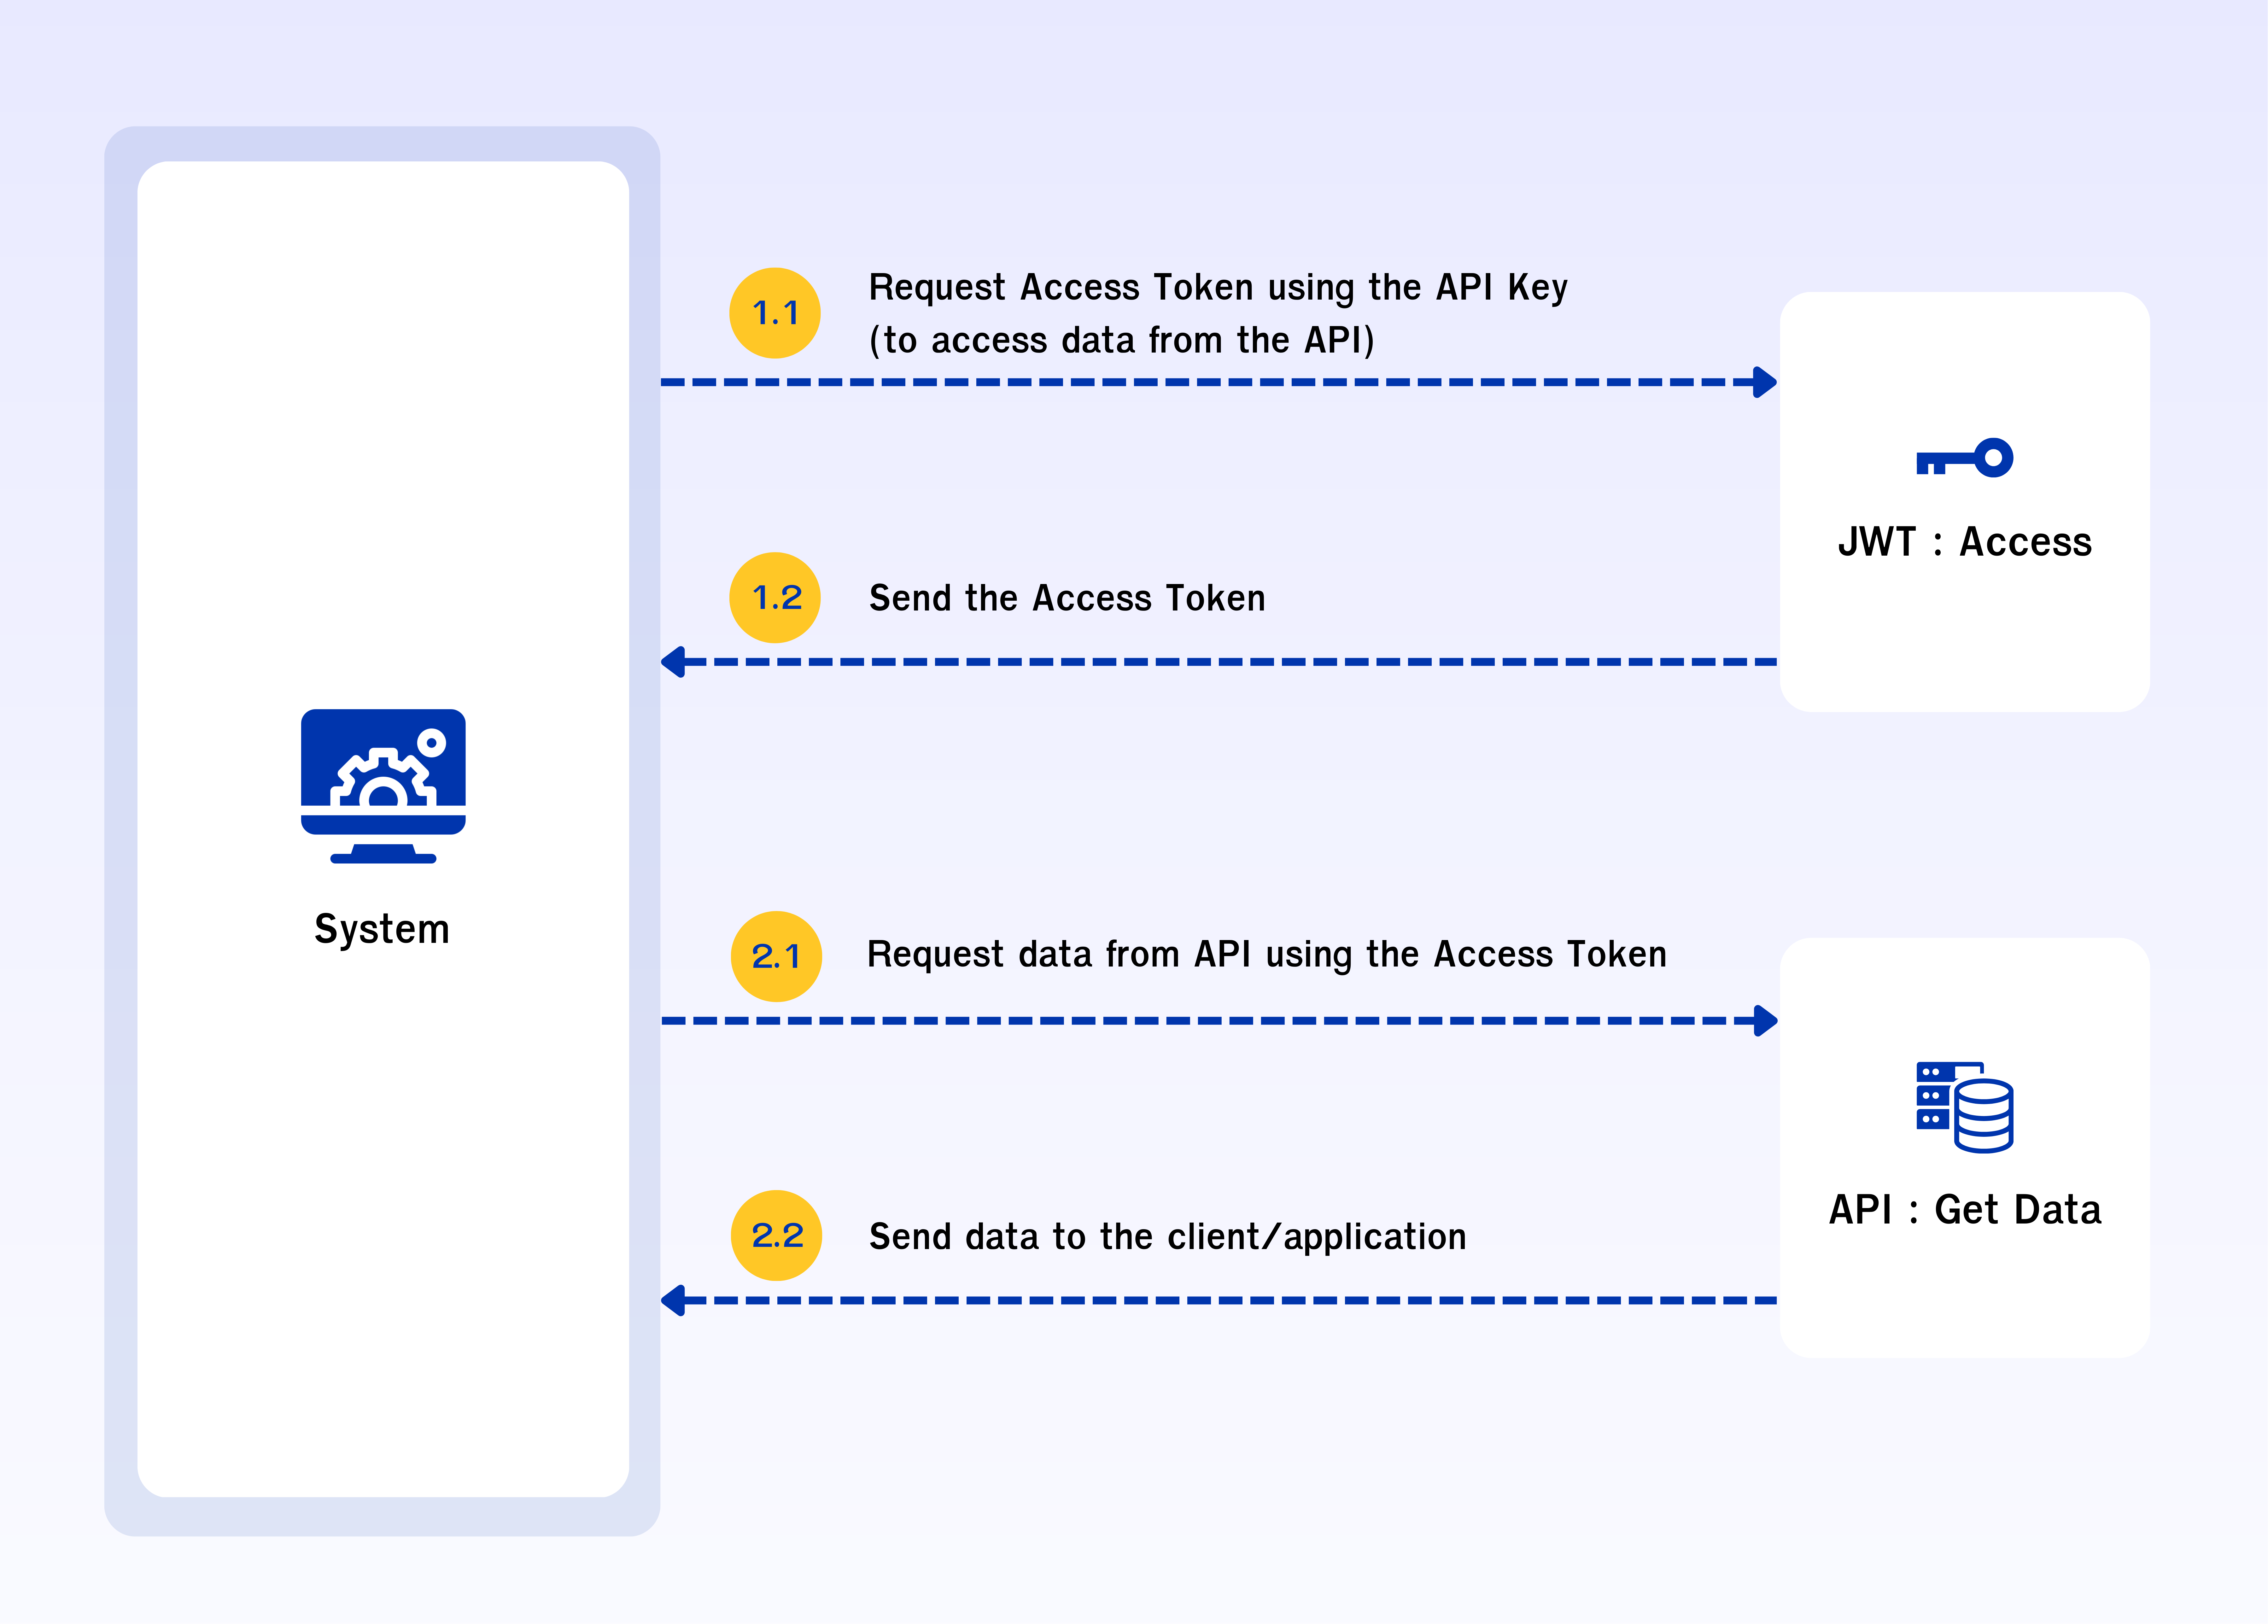
- System use for generate token key.
-
Method /v1/access/
- Get token access, with used API Key. And get token access for access API.
- Token access has expired in 3 minutes.
- Recommend to use token access for access API in 1 time, and request new token access for use API in next time.
-
Package
- No Package.
-
Example
- Path
- {domain}/v1/access/{APIKey}
- {domain}/v1/access/{APIKey}?correlationId={UUID}
- Path
- Get token access, with used API Key. And get token access for access API.
-
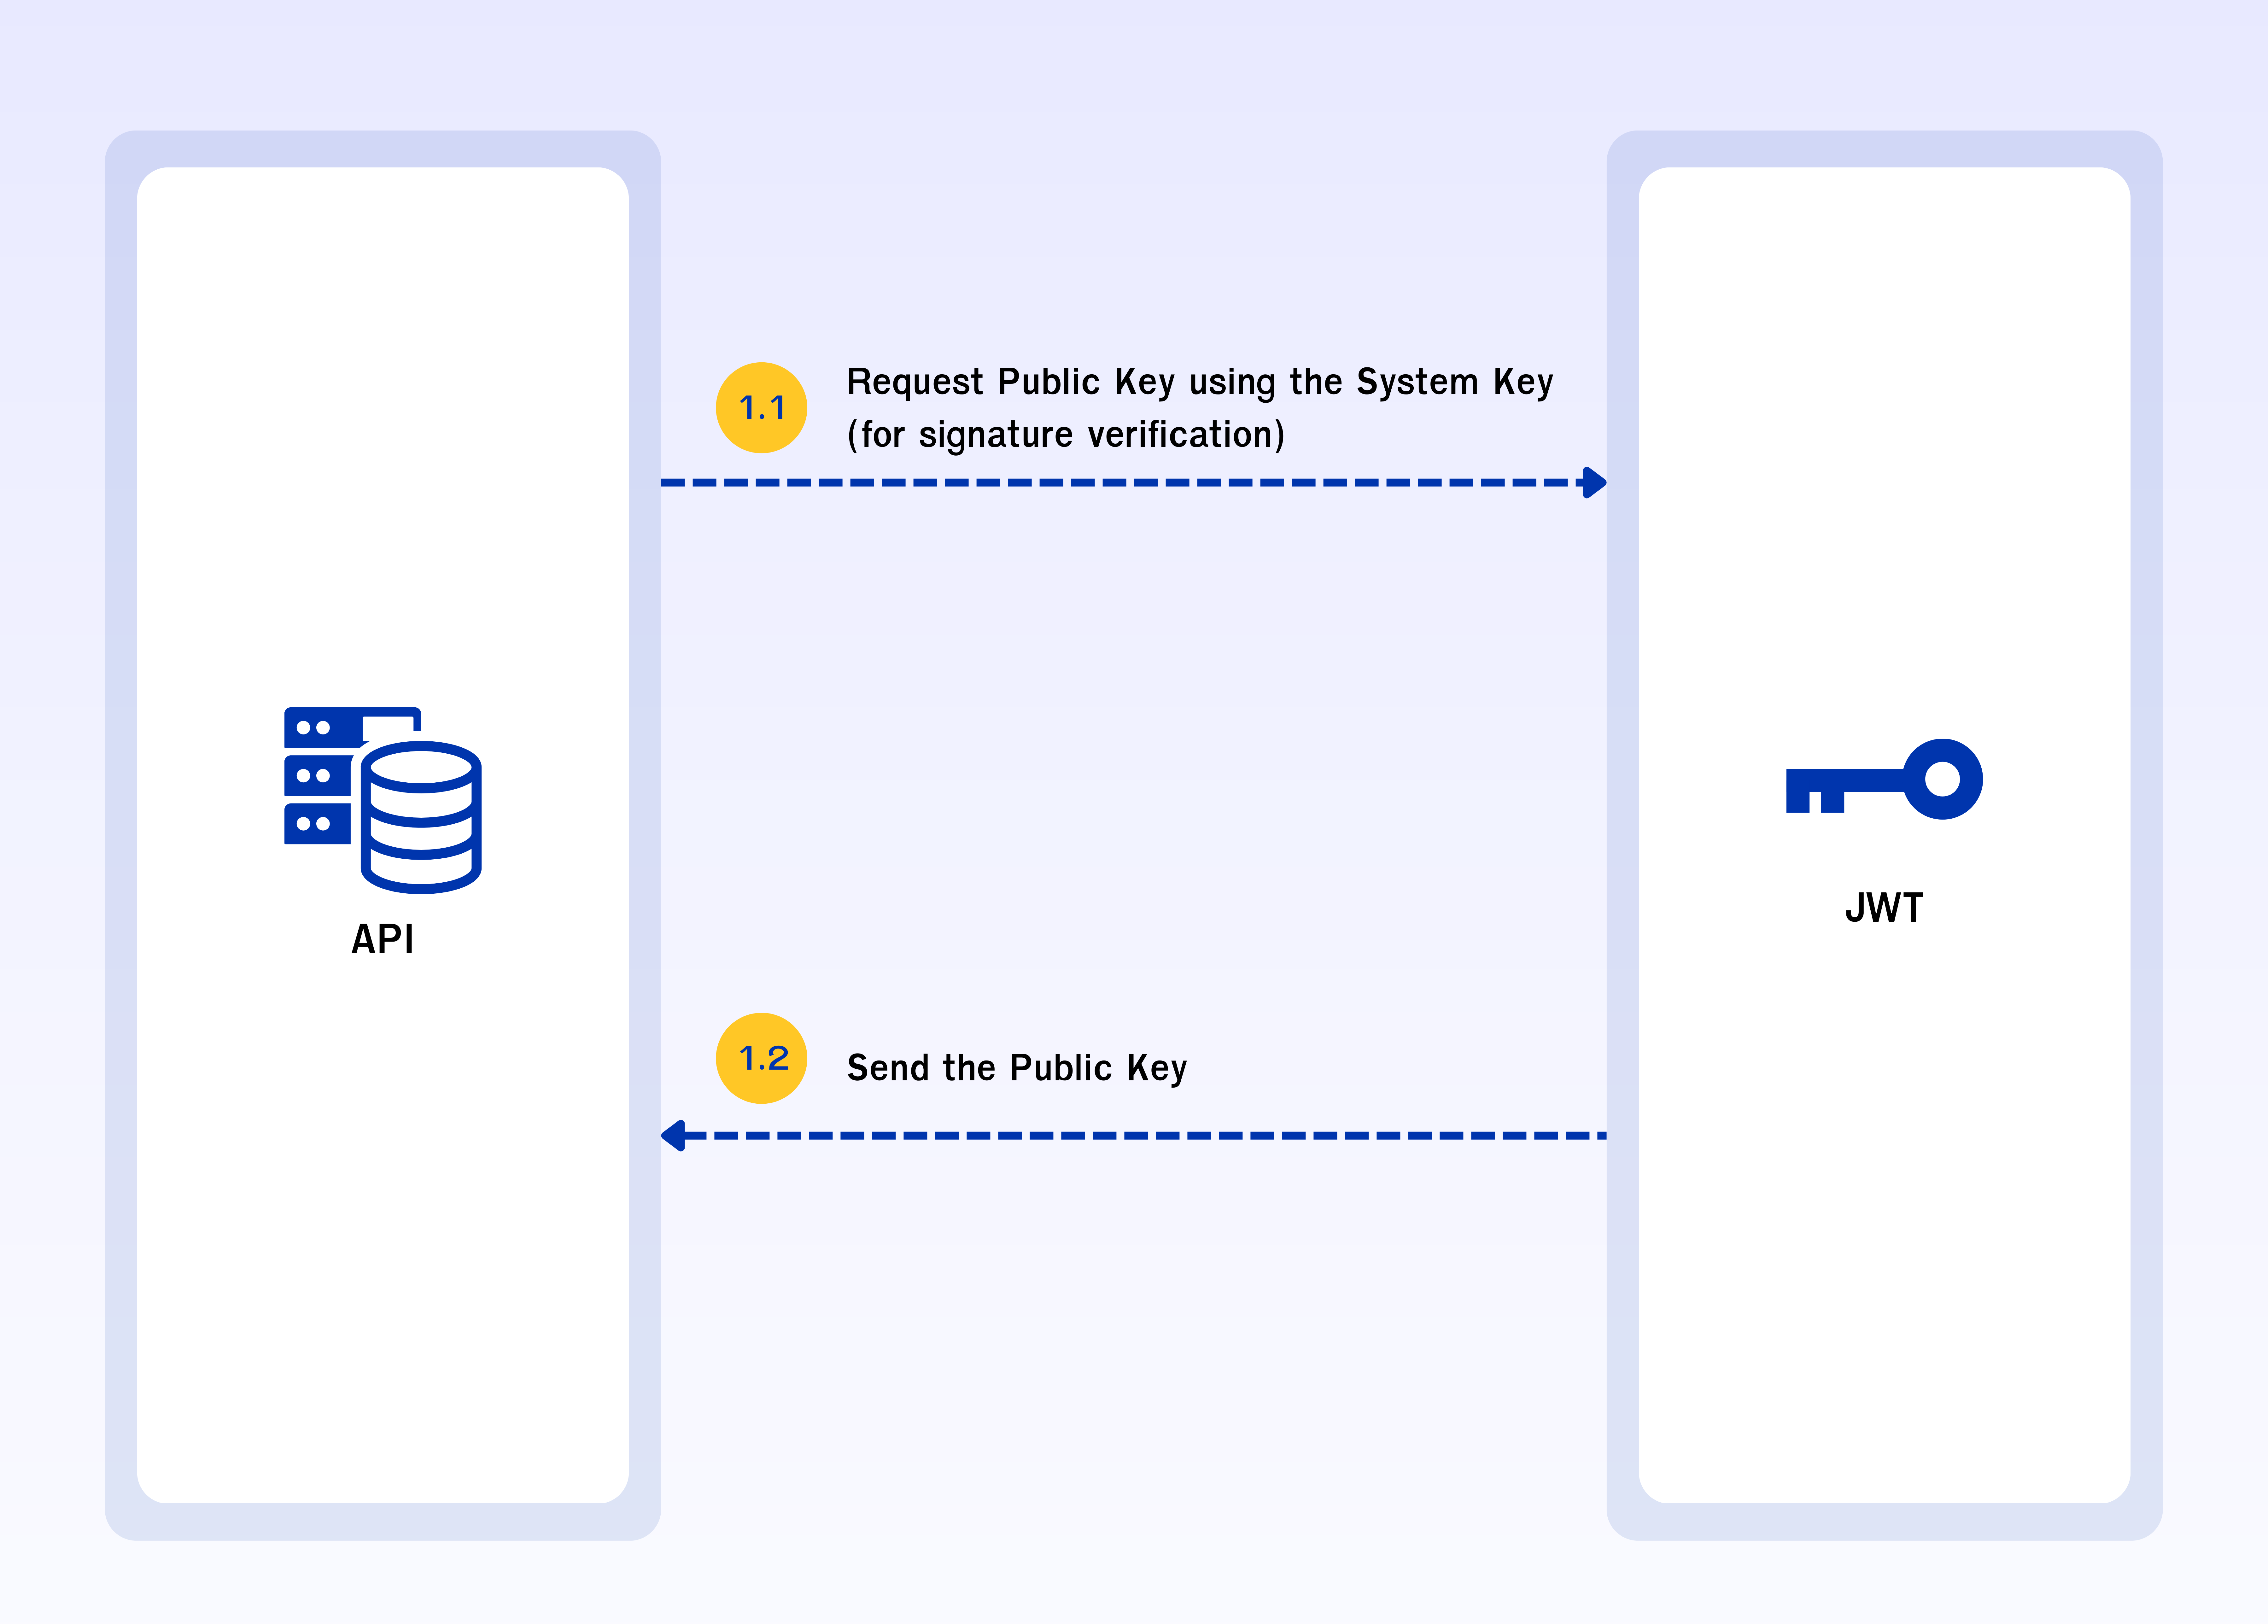
- API Service use for verify signature from token access.
-
- Get public key for verify signature token access.
- Document & libraries
-
Package
- Base64 all parameter, with “.” (dot).
-
tokenAccess
- Used Data “tokenAccess” from package request API Authorization.
-
systemKey
- System key
-
Example
- Path
- {domain}/v1/publickey (package with header)
- {domain}/v1/publickey?package={package}
- {domain}/v1/publickey?package={package}&correlationId={UUID}
- Path