Snyk Dependency Scanning - 310-Blueprint/fairshare GitHub Wiki
Snyk dependency scanning
Current setup
- Setup date: 24 August 2026
- Tracking issues: #21 and #62
- Monitored target:
se310-fairshare/fairshare - Integration type: GitHub Cloud App
- Monitored manifests:
backend/pom.xmlandfrontend/package.json - Test frequency: daily automated retesting
- Automatic Fix PRs: enabled for new vulnerabilities and known vulnerabilities (backlog)
- Fix PR strategy: one PR per vulnerability
- Pull request checks: enabled for Snyk Open Source security and licenses
The GitHub Cloud App can create remediation pull requests without storing a Snyk token, GitHub personal access token or other credential in the repository. The option to fix all vulnerabilities for the same dependency in one pull request is disabled.
Current scan
| Manifest | Package manager | Dependencies | Result |
|---|---|---|---|
backend/pom.xml |
Maven | 88 | 0 issues |
frontend/package.json |
npm | 7 | 0 issues |
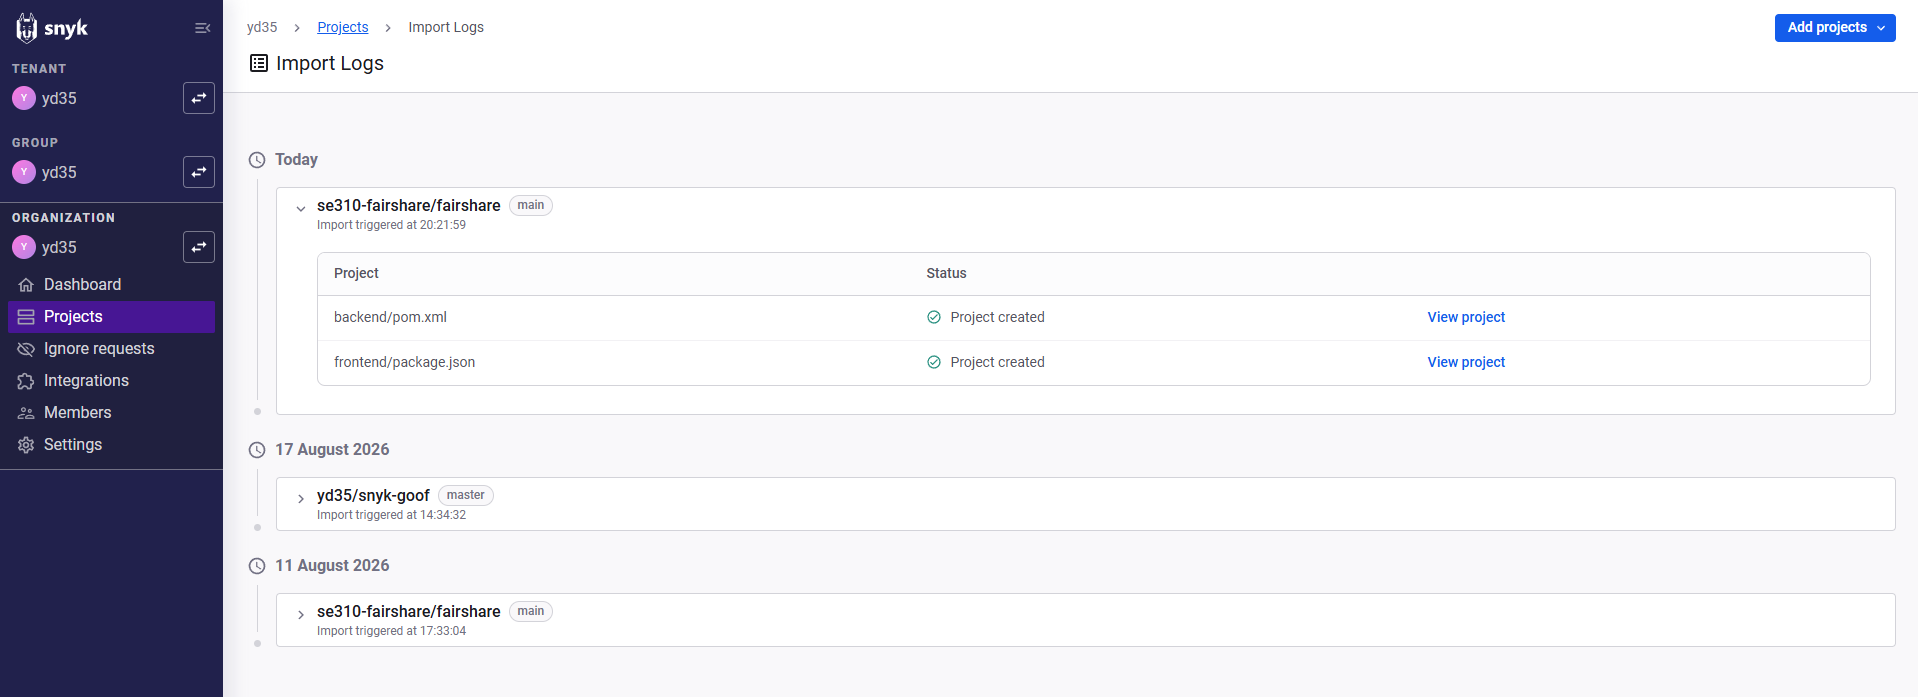
Both projects were imported and tested successfully on 24 August 2026. Snyk did not create a Fix PR because neither project currently has a vulnerability. If a compatible fix becomes available for a new or known vulnerability, Snyk is configured to create a separate Fix PR. Each Fix PR must still pass the normal test and review workflow before it is merged.
Setup evidence
The import log confirms that Snyk created projects for both manifests.
The backend project was tested through the GitHub Cloud App and reports no issues.

The frontend project was tested through the GitHub Cloud App and reports no issues.

Previous scan and remediation
The original read-only setup under issue #21 found eight transitive backend vulnerabilities and no frontend vulnerabilities. The backend findings were tracked through issues #30, #31, #32 and #33. The current scan reports zero issues for both manifests.
Issue #62 replaced the read-only setup with the GitHub Cloud App so Snyk can create the automatic remediation pull requests required by the assignment.
Verification procedure
- Open the Snyk project dashboard and confirm both manifests are active.
- Confirm each project shows
Open on GitHub Cloud Appand has a recent successful snapshot. - Confirm automatic Fix PRs are enabled for new vulnerabilities and known vulnerabilities.
- Confirm
Fix all vulnerabilities for the same dependency in a single PRremains disabled. - Review and test any Snyk Fix PR before merging it.
References
- Snyk GitHub Cloud App
- Automatic Fix PRs for new vulnerabilities
- Automatic Fix PRs for known vulnerabilities
Generative AI assisted with editing this page. The Snyk configuration, imported manifests and scan results were manually reviewed and verified.